SecMap
See how your applications work. Know where to look for risk.
DryRun SecMap is a security context graph of your repository. It connects application features and security controls to the code behind them, giving your team application knowledge it can inspect and reuse.
Follow the connections
See the code behind the connections.
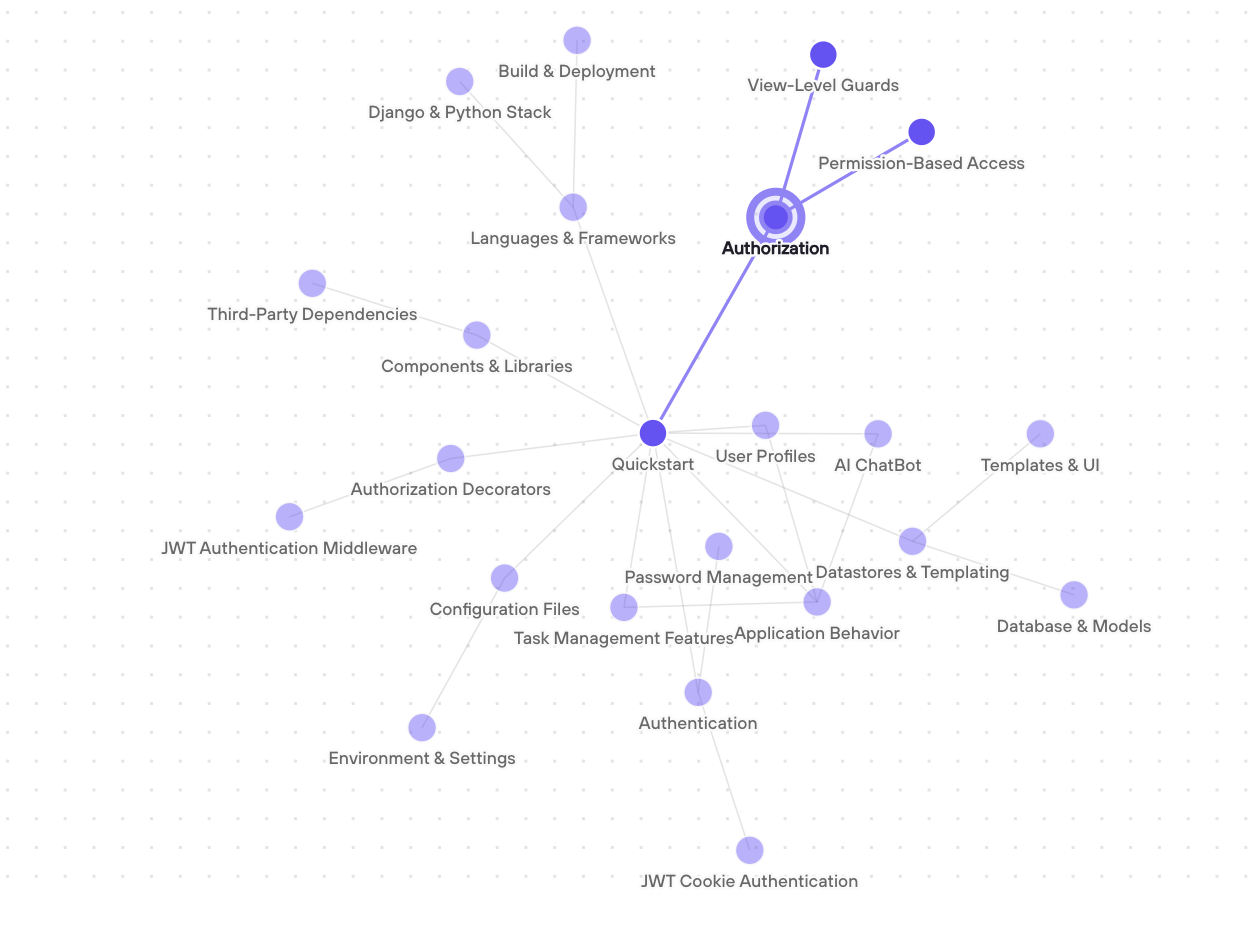
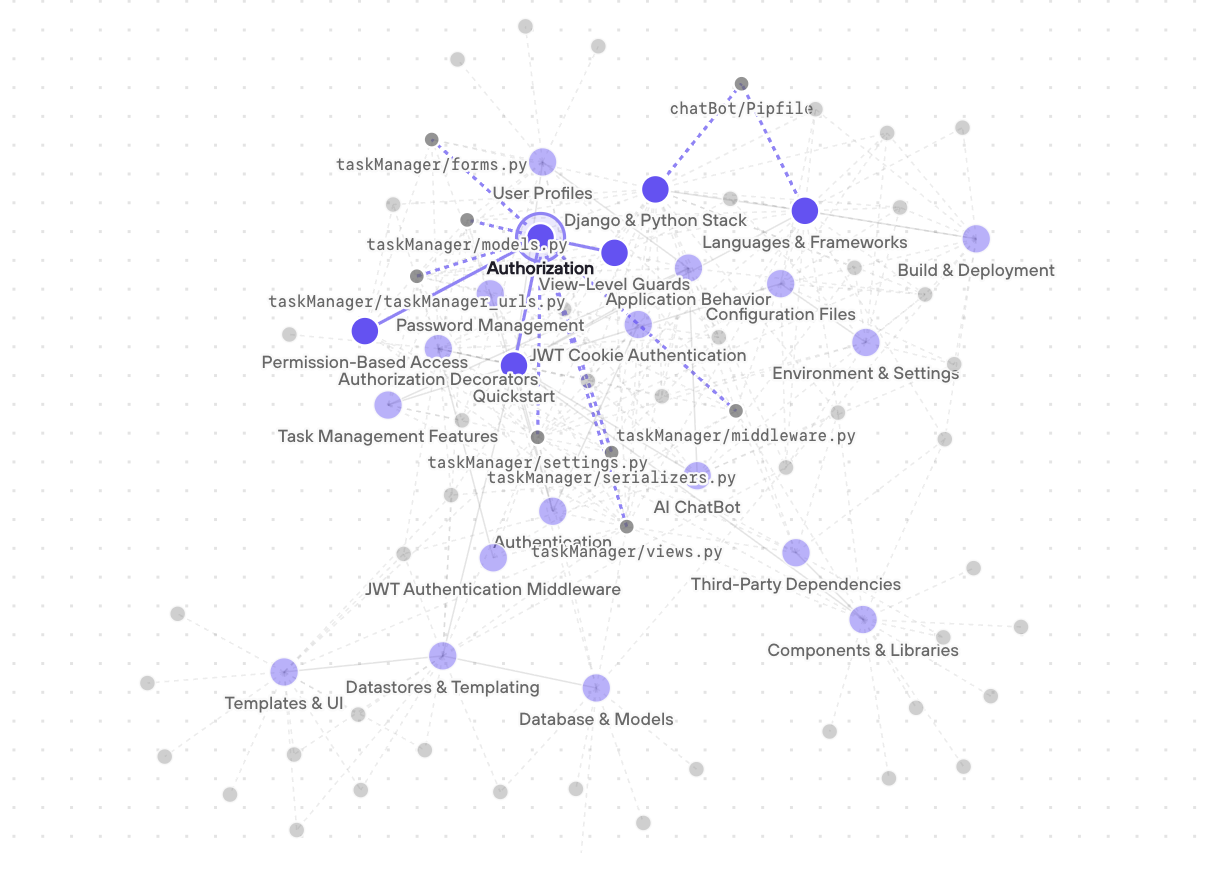
A SecMap turns repository context into a view you can explore. Select a feature or security mechanism, follow its relationships, and bring the source files into view.
Here, Authorization connects to View-Level Guards, Permission-Based Access, and their source files. Use those connections to focus an investigation, bring a reviewer up to speed, or ground a threat model in the code.
Separate example · AI ChatBot
Inspect a claim at its source.
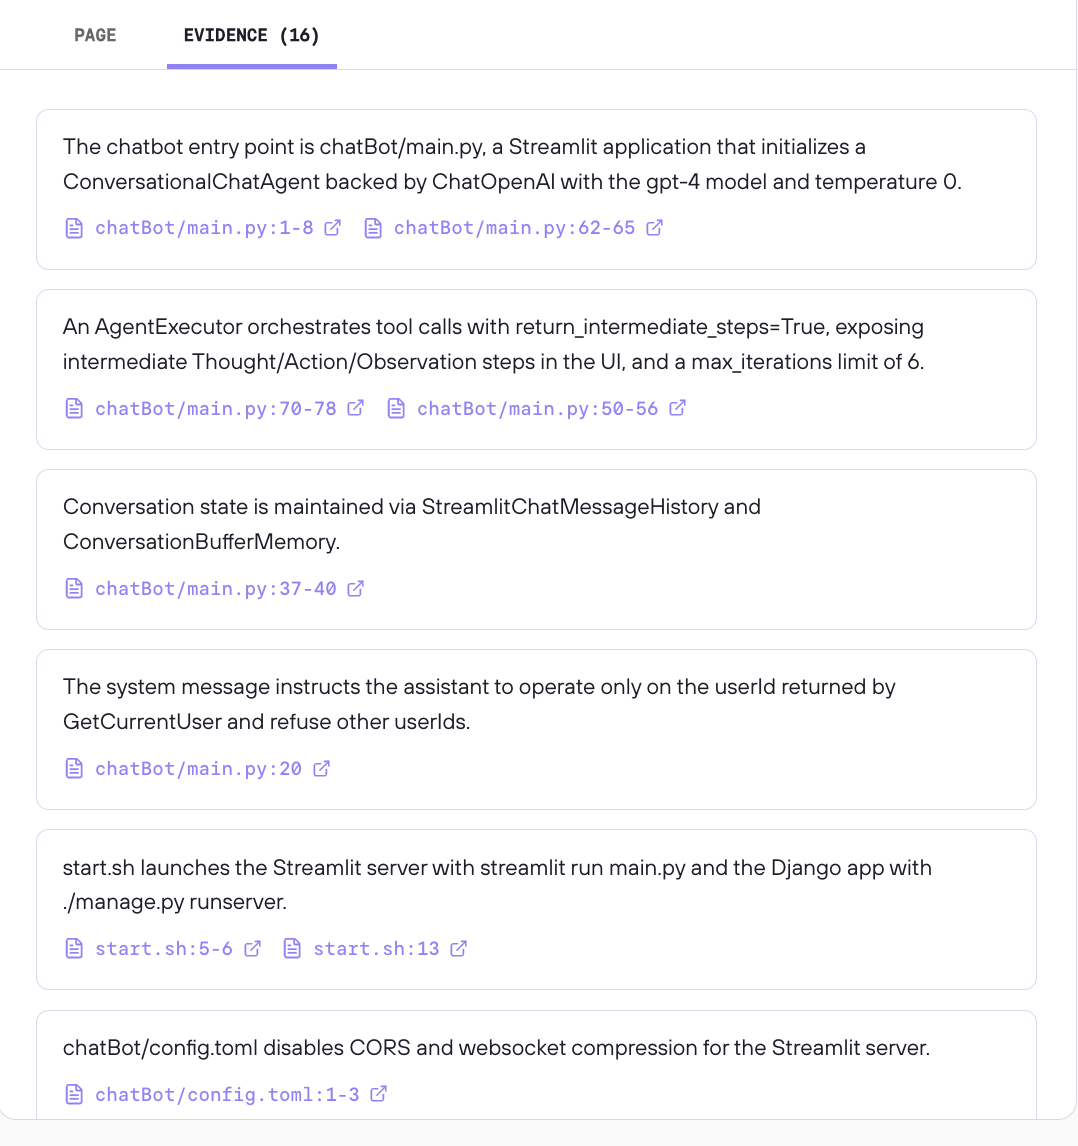
Open a topic’s evidence to see what DryRun found and where it appears in the code. Source-file references and line ranges, where provided, let you inspect the implementation at the analyzed revision.
Here, the AI ChatBot evidence describes the agent’s entry point, tool execution, and conversation memory, with references back to their source files.
Application context
Knowledge your team can inspect.
As DryRun analyzes your repository, it maps how your application fits together: its features, its security mechanisms, and the code that connects them. SecMap puts that map in front of your team, so you can trace how the app is built and check the evidence behind every relationship.
Context from your pull requests
PR reviews investigate changes with the surrounding application in view. That analysis contributes to the repository’s security context.
Explore PR code reviewsA baseline across the repository
DeepScan analyzes the existing codebase to build a security baseline. Use it to deepen your understanding of the code already there.
Explore DeepScanSee the evidence behind the graph.
Explore SecMap with the DryRun team.
Get a DemoHave a question about your code? Explore Codebase Intelligence for answers grounded in your repository and findings.