Helping teams keep credentials out of Git at:
2X
More Accurate
We’re the most accurate SAST you can get in a PR. Going beyond regex and pattern libraries, DryRun Security inspects data flow across files and services.
90%
Custom Policy Agent
The Contextual Security Analysis engine reasons about exploitability and impact, not just the presence of a pattern.
0
No Rules to Maintain
No more regex or brittle rule groups that take hours to create, validate, and keep up to date. You get AI-driven, custom policy checks in every PR.
A different approach
Compare the approaches
| Capability | Legacy SAST | DryRun Security | Benefits | |
|---|---|---|---|---|
| 1 | Low Noise | No | Yes | Contextual, agentic reasoning tells real credentials from test data, sample keys, encrypted blobs, and scrubbed values—cutting false positives so developers focus on what matters. |
| 2 | Best Risk Coverage | No | Yes | Finds hard-coded secrets across app code, configs, CI/CD, and IaC. Provider-aware patterns (API keys, tokens, signing material) plus Contextual Security Analysis catch obfuscated uses (e.g., concatenation, base64, logging). |
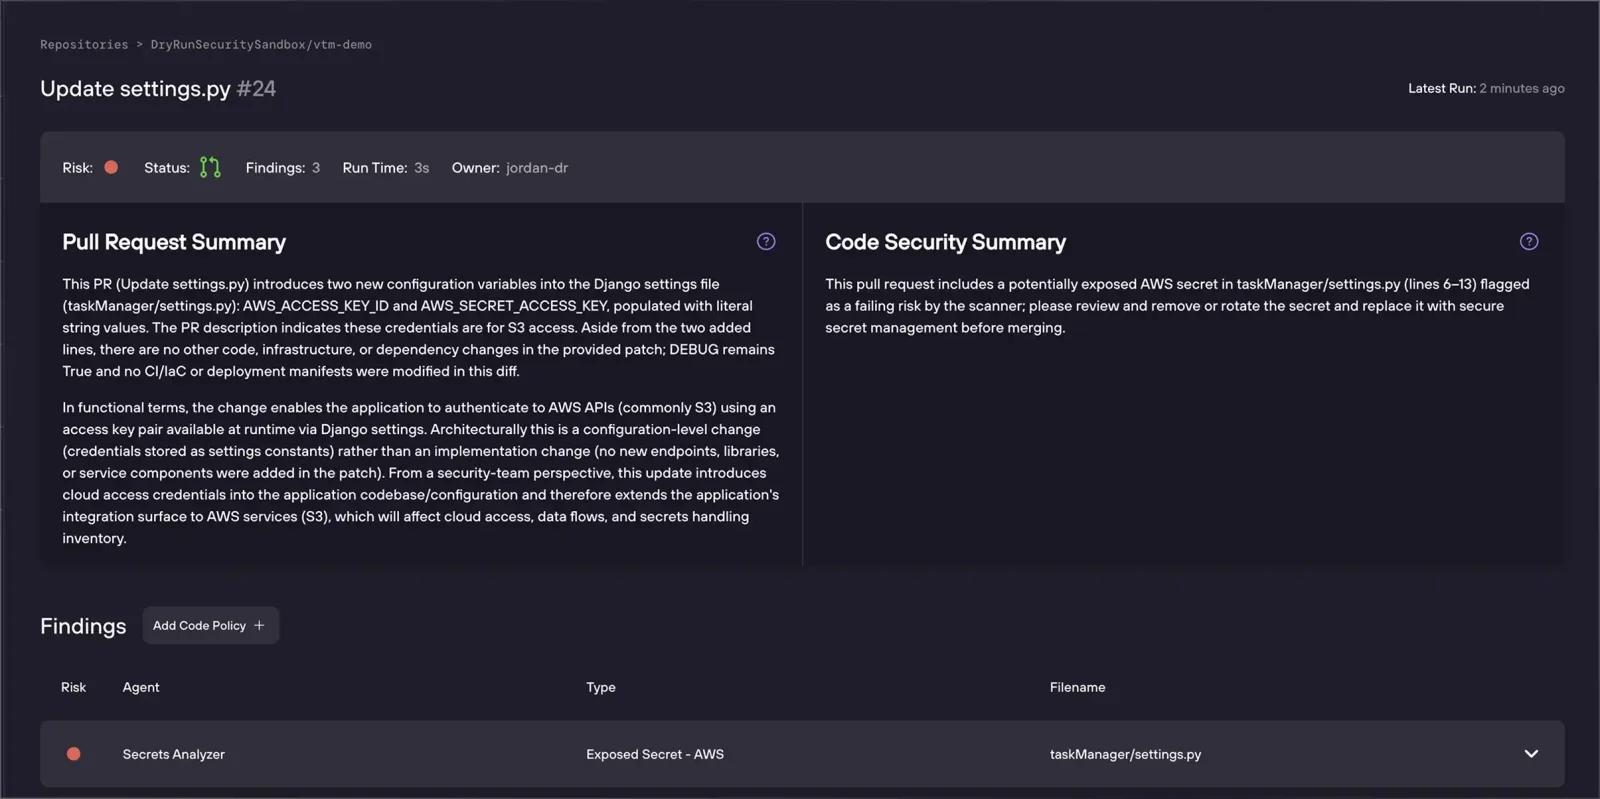
| 3 | Actionable Guidance | No | Yes | Inline PR feedback shows the secret, the path of exposure, and clear next steps, including automated policy exclusions when appropriate. |
| 4 | Fast Feedback | No | Yes | Runs on every PR. The Custom Policy Agent enforces Natural Language Code Policies to block risky merges with explanations developers can act on in seconds. |
| 5 | Code Insights | No | Yes | Org-wide trends for secret incidents, hotspots, and time-to-remediate across repos and teams—powered by the Codebase Insight Agent and actionable via MCP-enabled automation. |
How it works
How DryRun Security AI-Native SAST Works
PR created
The PR event triggers DryRun Security to review the change along with relevant files for context.
Expert Agents Collaborate
The Code Review Agent runs Contextual Security Analysis while our Custom Policy Agent applies your policies. They coordinate specialized sub-agents, validate exploitability, and add repo context as needed.
Surface Only What Matters
In under a minute (typical), developers receive tailored PR feedback with precise code references and remediation steps, while AppSec gets a separate executive-style summary of findings, policy outcomes, and compliance impact.
AppSec expertise. Put to work.
Powered by the DryRun Security Agents
DryRun Security is unlike any SAST you’ve seen before. It’s powered by our:
Code Review Agent
Runs Core Code Policies on every PR and gives developers real-time, contextual feedback.
Custom Policy Agent
Enforces your custom Natural Language Code Policies alongside standard and advanced contextual SAST checks.
Codebase Insight Agent
Instead of stitching together dashboards and exports, you ask real questions in natural language and get precise, contextual answers about risk, trends, and exposure across your repositories.
Credential coverage
DryRun checks pull requests for exposed credentials, including API tokens, private keys, and database connection strings. It attempts to verify whether a detected secret is active. See credential types and verification and PR language support.
Integrations
DryRun Security connects with your AI coding tools, source control, and team communication tools so security review fits into your development workflow.
Ready to Meet Your AppSec Agents?
Static analysis tools tell you what might be wrong. DryRun Security shows you what actually matters.
No sales script. No generic demo loop. Just a conversation about your code, your team,and how to level up your AppSec program.