Trusted by engineering and security teams including:
DryRun Security Intelligence
Ask a question. Follow the evidence.
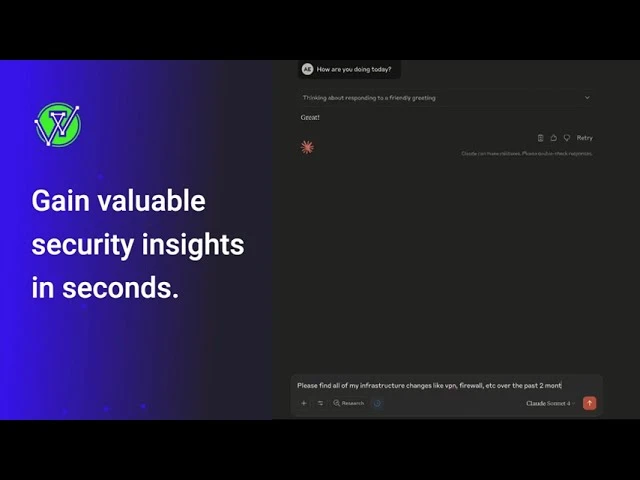
Chat with your security context inside DryRun. Investigate changes across repositories and get answers you can trace back to the code.
What changed in our attack surface this week?
Intelligence connects the context
Two new entry points. Here’s where to look.
Review who can export a customer’s records.
routes/customer-exportCheck the permission boundary for admin reports.
routes/admin-reportWith DryRun Security, it feels like we’ve more than doubled our AppSec team. We can focus on the pull requests that truly matter, thanks to Code Insights. What’s more, our developers get instant, actionable guidance on writing secure code — it’s like having a security coach in every pull request. The tool has transformed how we approach application security, scaling our efforts without adding headcount or slowing development.
Sean Holcroft
Application Security Architect
Questions from our customers
Start with what you need to know.
Explore the changes behind a new attack surface, or bring the bigger picture into your next security review.
You ask
Did we add any new Go HTTP endpoints this week or last?
Trace new entry points
Follow a new endpoint to the change that introduced it and the access boundary that needs review.
You ask
Tell me the top 5 features we shipped this month that have the most risky security implications. Link me to the PRs.
Connect features to security implications
Bring the security implications of shipped features into the conversation, with the changes behind them.
You ask
Make a chart with vulnerabilities by type. Show just the top 3 risky ones.
Find the recurring themes
See which categories need attention, then investigate the findings behind the trend.
You ask
List any PRs related to Lambda URLs in the last month.
Find changes that match your question
Find a specific infrastructure change across repositories without assembling the history by hand.
You ask
Where did we introduce high-risk findings this week?
New high-risk findings by repository
See where risk is entering your codebase, then follow the findings to the changes behind them.
Finding infrastructure changes
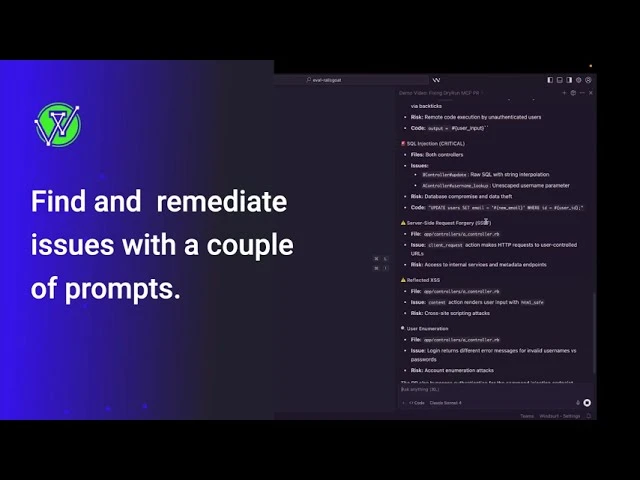
Automating Discovery and Remediation
How it works
How DryRun Security AI-Native SAST Works
PR created
The PR event triggers DryRun Security to review the change along with relevant files for context.
Expert Agents Collaborate
The Code Review Agent runs Contextual Security Analysis while our Custom Policy Agent applies your policies. They coordinate specialized sub-agents, validate exploitability, and add repo context as needed.
Surface Only What Matters
In under a minute (typical), developers receive tailored PR feedback with precise code references and remediation steps, while AppSec gets a separate executive-style summary of findings, policy outcomes, and compliance impact.
AppSec expertise. Put to work.
Powered by the DryRun Security Agents
DryRun Security is unlike any SAST you’ve seen before. It’s fueled by our:
Code Review Agent
Runs Core Code Policies on every PR and gives developers real-time, contextual feedback.
Custom Policy Agent
Enforces your custom Natural Language Code Policies alongside standard and advanced contextual SAST checks.
DryRun Security Intelligence
Ask questions in product and get answers grounded in your repository context and security findings. Bring that context to your coding agents through integrations when it’s time to work on a fix.
Context across your stack
PR reviews and DeepScan identify the languages and frameworks in your repository. DryRun uses that context to connect findings to the code that matters. See language and framework support.
Integrations
DryRun Security connects with your AI coding tools, source control, and team communication tools so security review fits into your development workflow.
Ready to Meet Your AppSec Agents?
Static analysis tools tell you what might be wrong. DryRun Security shows you what actually matters.
No sales script. No generic demo loop. Just a conversation about your code, your team,and how to level up your AppSec program.