Trusted by engineering and security teams including:
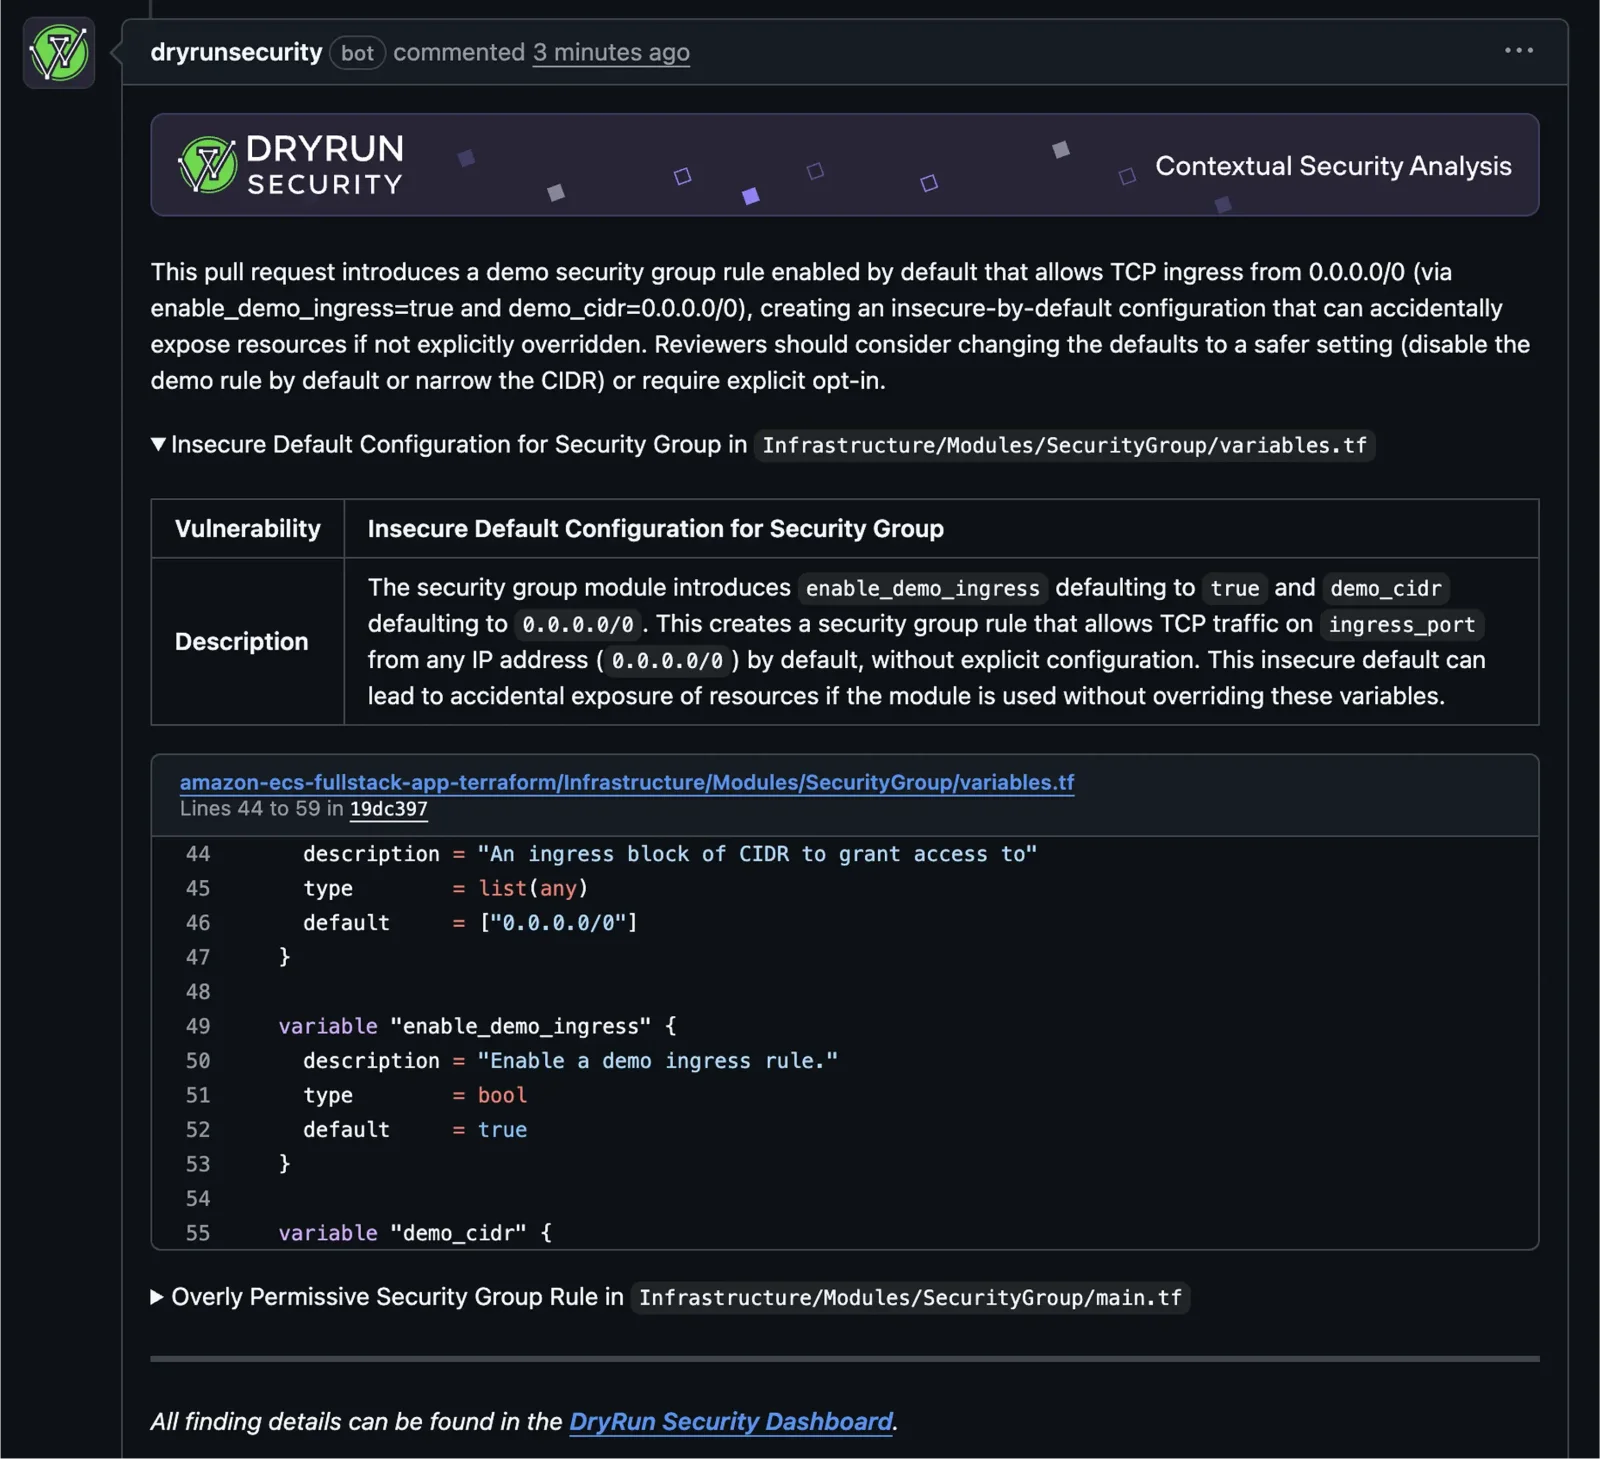
Context-aware misconfig detection
We look at infrastructure and application code as a system. That means we can flag the misconfigs that expose real data and workloads, not every theoretical issue.
Shift-left without surprise risk
Run IaC checks in PRs with clear guidance so teams can fix issues while they’re still designing infrastructure, not after a failed deployment.
Policy-driven guardrails
Use our natural language code policies to encode your cloud and platform guardrails (e.g., what can be public, which regions are allowed), and let the Custom Policy Agent enforce them on every change.
AppSec expertise. Put to work.
Powered by the DryRun Security Agents
DryRun Security is unlike any SAST you’ve seen before. It’s powered by our:
Code Review Agent
Runs Core Code Policies on every PR and gives developers real-time, contextual feedback.
Custom Policy Agent
Enforces your custom Natural Language Code Policies alongside standard and advanced contextual SAST checks.
Codebase Insight Agent
Instead of stitching together dashboards and exports, you ask real questions in natural language and get precise, contextual answers about risk, trends, and exposure across your repositories.
Infrastructure coverage
DryRun’s IaC scanner checks changed Terraform files for risks such as overly broad IAM permissions. For application code reviewed alongside your infrastructure, see source language and framework support.
Integrations
DryRun Security connects with your AI coding tools, source control, and team communication tools so security review fits into your development workflow.
Ready to Meet Your AppSec Agents?
Static analysis tools tell you what might be wrong. DryRun Security shows you what actually matters.
No sales script. No generic demo loop. Just a conversation about your code, your team,and how to level up your AppSec program.