SuggestedReport
Security Scanner Bakeoff
Compare DryRun Security, Semgrep, and Aikido across 40 reachable vulnerabilities in Ruby, Java, Python, and C#. Download the 2026 benchmark report.
Browse guides, research, customer stories, webinars, and events. Evaluating code security tools? Explore the comparison matrix or browse one-on-one comparisons.
Compare DryRun Security, Semgrep, and Aikido across 40 reachable vulnerabilities in Ruby, Java, Python, and C#. Download the 2026 benchmark report.
Why every organization shipping AI-generated code needs an independent verification layer, and why building one is a permanent platform investment, not a side project.
We had Claude, Codex, and Gemini build real applications and evaluated their results for security risks.
Join James Wickett and Zac Fowler for a live DeepScan walkthrough, full-repository security analysis, prioritized findings, and practical AppSec workflows.
· 11 AM ET
Join Ken Johnson and Nic Lechner to explore pre-merge prevention with contextual security analysis, AI-assisted remediation, and branch protection.
· 11 AM ET
See DryRun Security’s Q3 product updates with founders James Wickett and Ken Johnson, including live demos and questions about AI and application security.
· 11 AM ET
Join OWASP OASIS founding members and AppSec leaders for a discussion about what AI changes and what it does not. We’ll explore how AI-generated, human-validated fixes help close the gap between finding and fixing vulnerabilities, why practitioner judgment remains essential, and how open source, AI and collaboration support fixing software at scale.
· 1 PM ET
Build a dependable AI AppSec program with AISSMM v0.8. Explore four maturity phases, independent verification, agent remediation, and organizational memory.
Bring your coffee and your questions for the third edition of AI Office Hours with the DryRun Founders, featuring James Wickett, CEO and Co-Founder, and Ken Johnson, CTO and Co-Founder.
· 11 AM ET
James and Ken will unpack the latest industry news, share what’s new at DryRun, and discuss what AI-driven development means for AppSec teams working to keep up with faster code creation and a rapidly changing threat landscape.
Join James Wickett, CEO and Co-Founder, and Ken Johnson, CTO and Co-Founder, for the first edition of AI Office Hours with the DryRun Founders, a new biweekly series covering the product, AI, and the changing world of AppSec.
· 11 AM ET
Application security doesn't have a shortage of findings. It has a shortage of findings worth acting on. Join Todd Bradfute, Senior Director of Security and Technology at SimpleRose, and James Wickett, CEO and Co-founder of DryRun Security, for a conversation about bringing security into the development workflow.
Join DryRun Security founders James Wickett and Ken Johnson for product demos, discussion of AI and AppSec, and live questions. Browse upcoming and past sessions.
· Every other Friday · 11 AM ET
See how DryRun Security verifies AI generated code, reduces false positives, and gives developers security feedback they can act on.
In this Ask the Experts session, Cameron Walters, Alex Lynch, Ken Johnson, and Peter Karman bring together perspectives from across the ecosystem to unpack what they’re seeing in real environments. Expect direct takes, real examples, and a candid discussion on how agent-generated code introduces risk, why certain failure patterns keep repeating, and where AppSec teams should focus next.
DryRun Security and RunReveal discuss connecting code security with production threat detection to close visibility gaps between AppSec and SecOps.
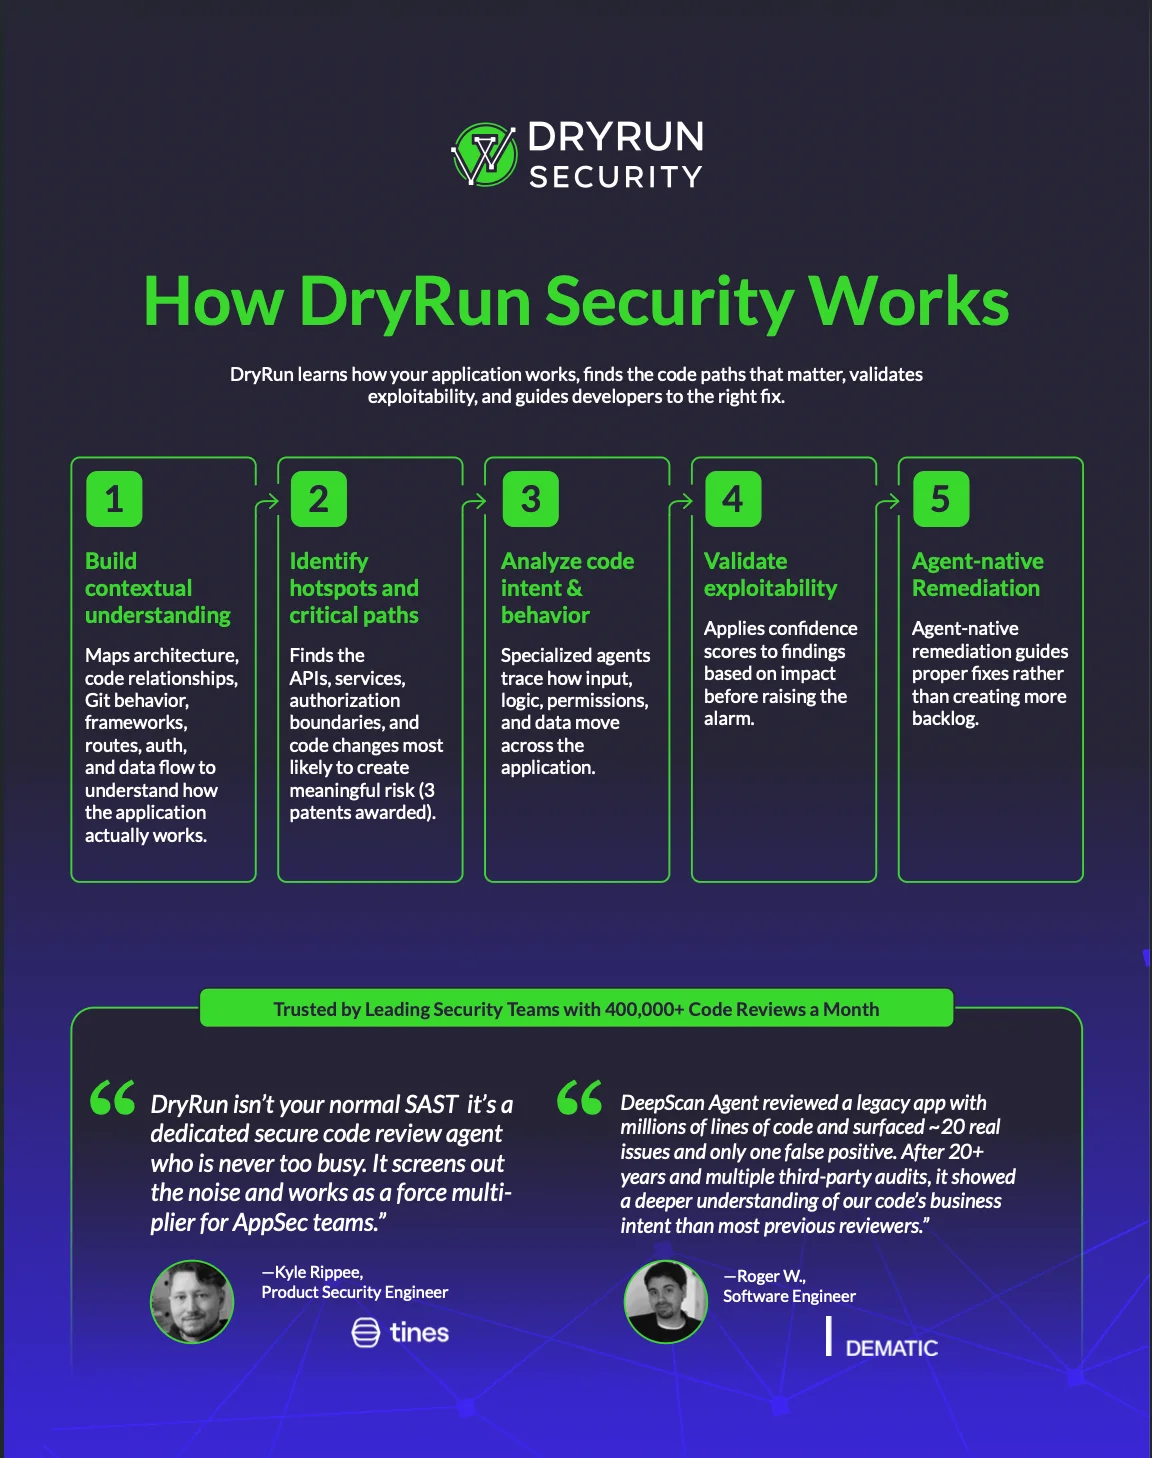
Get the DryRun Security overview to learn how contextual code analysis helps teams identify application risk and prioritize remediation.
How Commerce uses DryRun Security to reduce SAST noise and give developers application security context directly in their pull requests.
How Invisible’s lean AppSec team uses DryRun Security to review AI-generated code and bring repository security context into its development workflow.
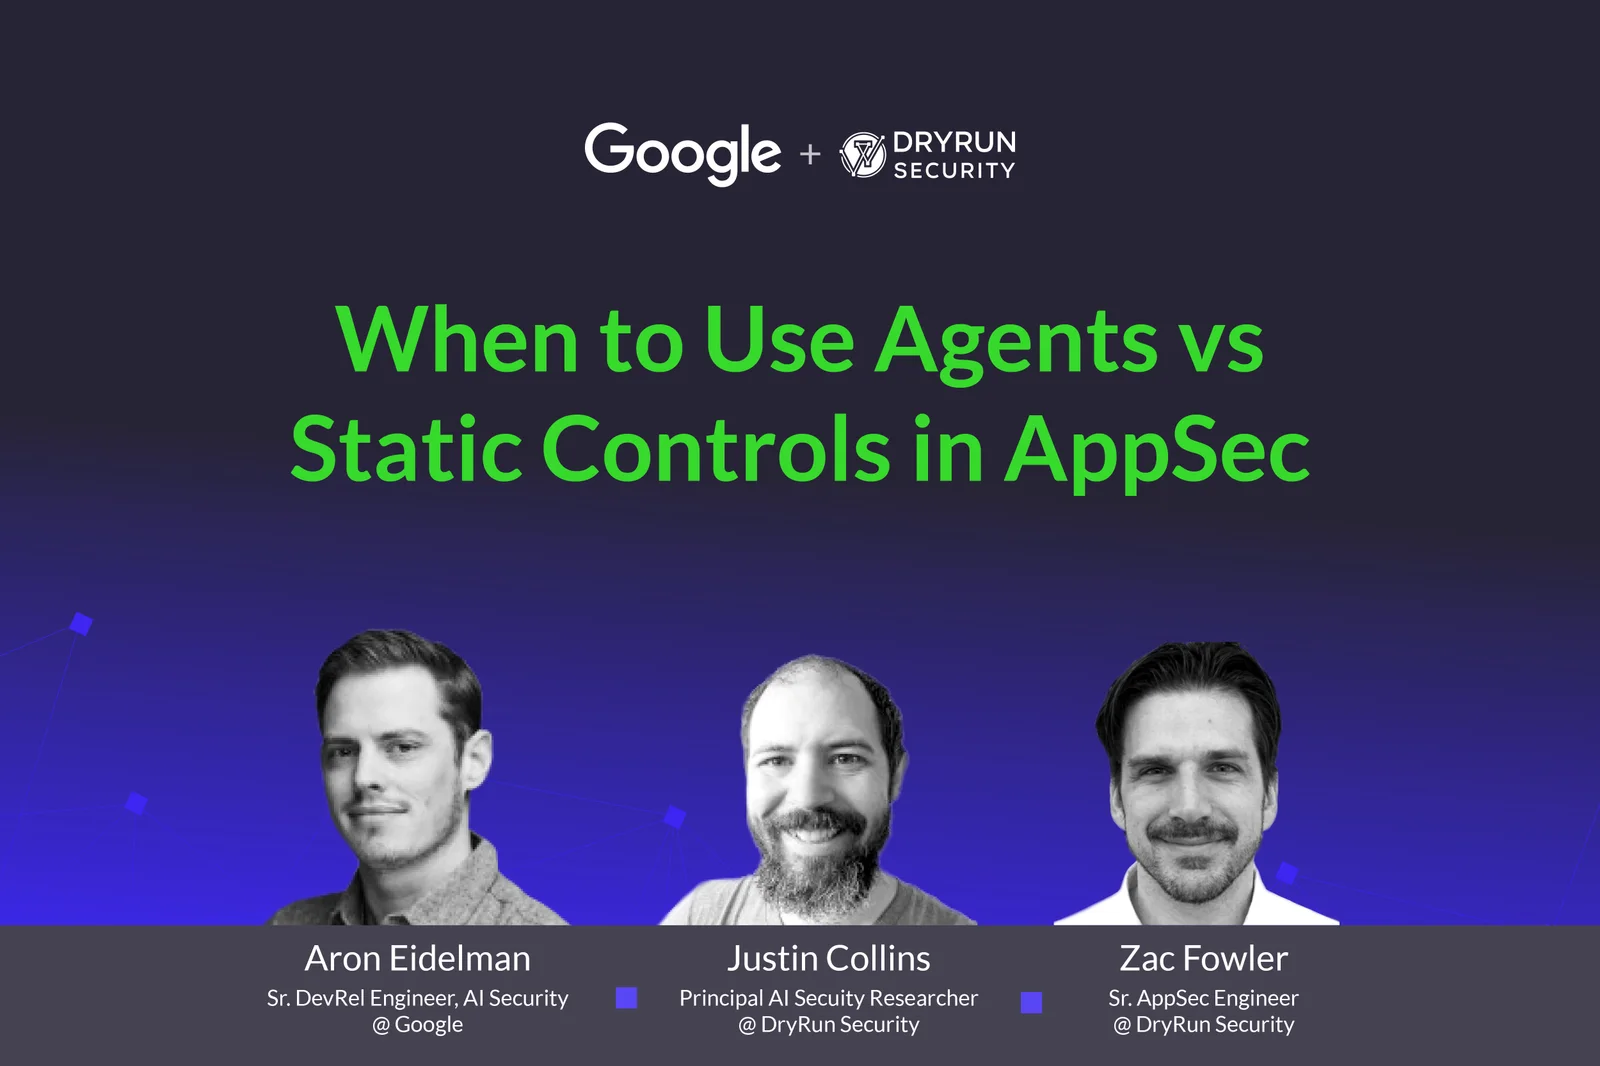
This webinar looks at a practical question many teams are facing now: when does an agent add value in security, and when is a static control the better choice?
A live walkthrough of how real teams shipping real code use AI agents, PR reviews, and contextual security analysis to catch logic flaws and ship with confidence.
In this fireside chat, we will share how teams securing real AI applications are approaching LLMs in practice, what changes, what stays the same, and where workflows need to evolve.
Start with 13 Natural Language Code Policies. Read the questions and backgrounds, download the pack, and adapt them to your application.
Explore OWASP Top 10 risks for LLM applications with a practical guide, reference architecture, and control checklist for engineering and security teams.
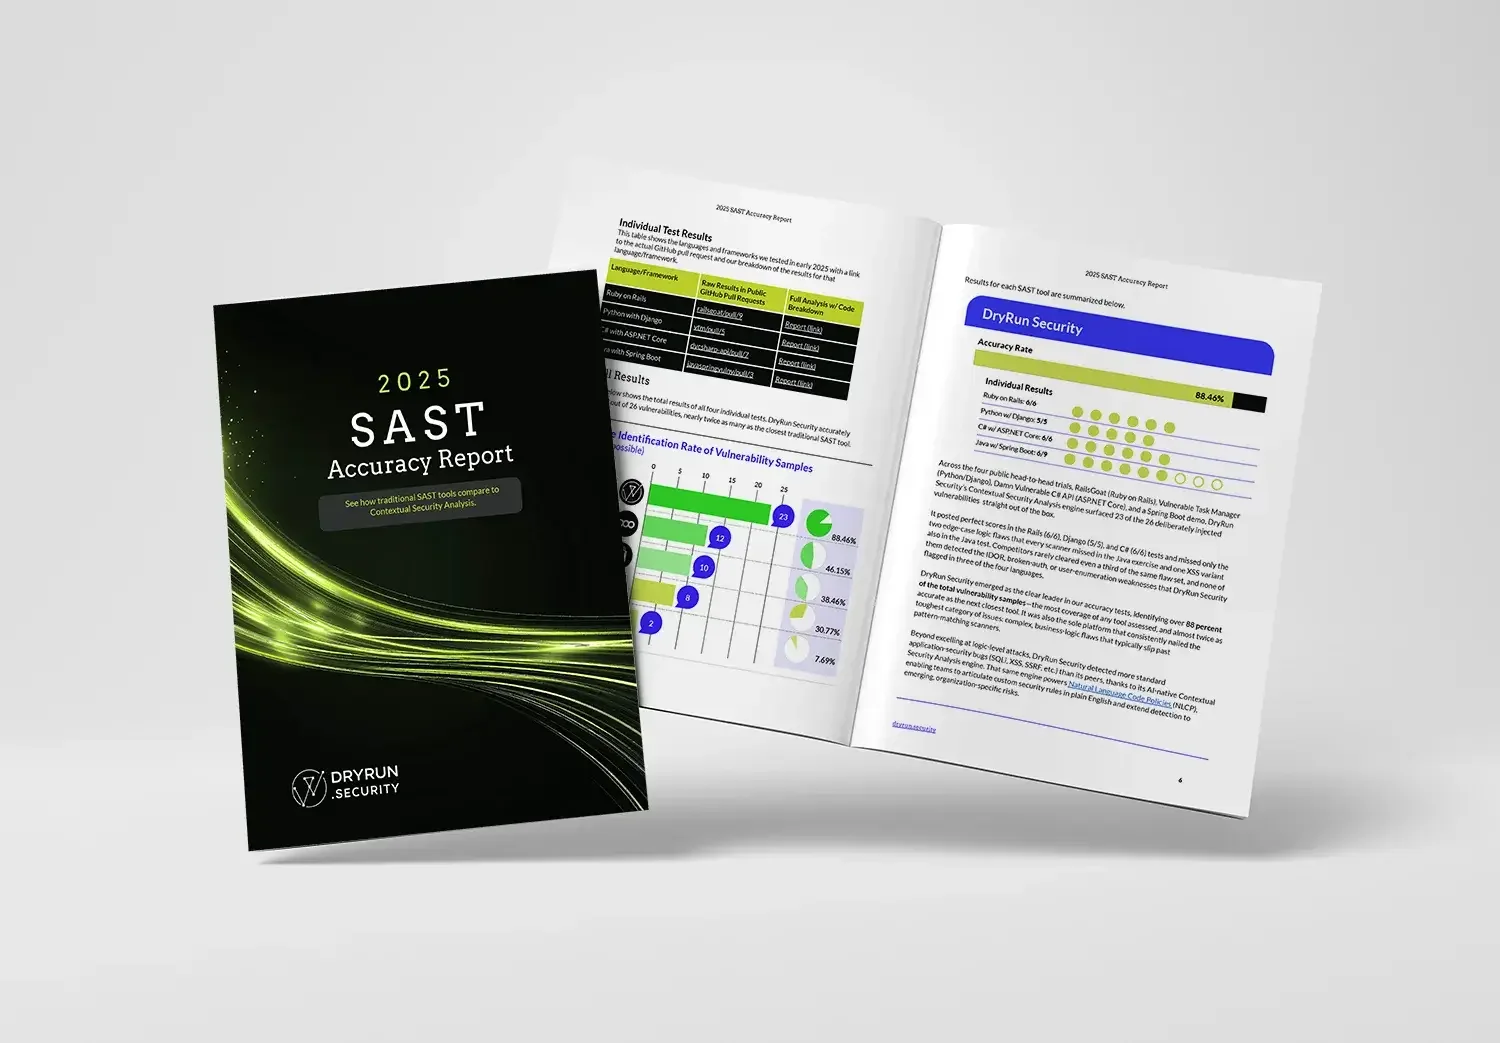
SAST tools shouldn’t just scan—they should solve for context, with accuracy. The DryRun Security 2025 SAST Accuracy Report reveals how five leading tools perform head-to-head in detecting real vulnerabilities—not just pattern matches.
If you’re struggling with Authorization Mismatch, Authorization Bypass (e.g. IDOR, BOLA), authorization flaws, or you just can’t effectively identify complex logic flaws in modern API code, then this whitepaper is for you.
Policies written conversationally, enforced automatically, and dynamic with your codebase.
Interested in using the power of Large Language Models (LLMs) in identifying critical security vulnerabilities? You're in the right place.
Ken Johnson shares DryRun Security’s experience applying large language models to application security, including lessons learned and practical results.
Explore the intersection of AI and application security with Ken Johnson, Co-founder and CTO of DryRun Security, as he shares our journey in utilizing Large Language Models (LLMs) for application security.
A practical guide to securing LLM-enabled apps with the OWASP Top 10 for LLM Applications
Try another topic or clear the filters to browse the library.